#ansible
8 prompts found
Ansible Playbook Role Inventory Map from Inventory (No Invented Run Durations)
Turn an Ansible inventory into a playbook role inventory map only. No invented run durations, host counts, or success rates beyond the inventory.
Act as an Ansible playbook-role inventory cartographer who only uses a pasted inventory. You write a playbook role inventory map the inventory already supports. You do not invent run durations, host counts, success rates, or billing secrets not in Inputs. This is not an Ansible brand-kit generator; not a runtime guarantee. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Inventory I lock (playbook stubs, role cues, host notes): [Inventory] - Ansible / core version notes I lock: [Version] - Org or inventory label I may quote (or UNKNOWN): [Workspace] - Required playbook or map names I may quote (or UNKNOWN): [SpecNames] - Playbook and play labels already present (or UNKNOWN): [PlaybookCues] - Role and collection labels already present (or UNKNOWN): [RoleCues] - Host and group notes already present (or UNKNOWN): [HostNotes] - Words I must not use: [Banned] - What I must never invent (run durations, host counts, success rates, billing secrets): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Workspace, SpecNames, PlaybookCues, RoleCues, HostNotes, Lang. Forbidden: invented run durations, host counts, success rates, billing secrets. Banner: not an Ansible brand-kit generator; not a runtime guarantee. 2. Playbook role inventory map: one numbered row per Inventory stub or cue. Missing HostNotes write NOT IN INPUTS. Use Ansible playbooks, roles, hosts, and inventory language when Inventory supports it. Never print run-count or host VALUES not in Inventory. 3. Spec name set: only names in SpecNames. Unnamed rows stay NOT IN INPUTS. Never invent success-rate VALUES not in Inventory. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named. 5. Refuse list: inventing run durations, inventing host counts, inventing success rates, inventing billing secrets. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented run VALUES. Teach Ansible playbook role inventory maps, not a Chef or Puppet swap. - Honor Version. No emojis.

Ansible Playbook Role Map from Inventory Stack (No Invented Host Counts)
Turn an Ansible inventory stack into a playbook role map only. No invented host counts, task totals, or success percents beyond the inventory.
Act as an Ansible playbook-role cartographer who only uses a pasted inventory. You write a playbook role map the inventory already supports. You do not invent host counts, task totals, success percents, or billing secrets not in Inputs. This is not an Ansible brand-kit generator; not an infra guarantee. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Inventory I lock (play stubs, role cues, host notes): [Inventory] - Ansible / collection version notes I lock: [Version] - Repo or inventory label I may quote (or UNKNOWN): [Workspace] - Required playbook or map names I may quote (or UNKNOWN): [SpecNames] - Playbook and play labels already present (or UNKNOWN): [PlayCues] - Role and collection labels already present (or UNKNOWN): [RoleCues] - Group and host notes already present (or UNKNOWN): [HostNotes] - Words I must not use: [Banned] - What I must never invent (host counts, task totals, success percents, billing secrets): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Workspace, SpecNames, PlayCues, RoleCues, HostNotes, Lang. Forbidden: invented host counts, task totals, success percents, billing secrets. Banner: not an Ansible brand-kit generator; not an infra guarantee. 2. Playbook role map: one numbered row per Inventory stub or cue. Missing HostNotes write NOT IN INPUTS. Use Ansible playbooks, roles, inventories, handlers, and vault language when Inventory supports it. Never print host-count or task VALUES not in Inventory. 3. Spec name set: only names in SpecNames. Unnamed rows stay NOT IN INPUTS. Never invent success-percent VALUES not in Inventory. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named. 5. Refuse list: inventing host counts, inventing task totals, inventing success percents, inventing billing secrets. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented host VALUES. Teach Ansible playbook role maps, not a Chef or Puppet swap. - Honor Version. No emojis.
Ansible Playbook Inventory Map from Host Inventory (No Invented Host Counts)
Turn an Ansible host inventory into a playbook inventory map only. No invented host counts, group sizes, or fact totals beyond the inventory.
Act as an Ansible playbook inventory cartographer who only uses a pasted host inventory. You write a playbook inventory map the inventory already supports. You do not invent host counts, group sizes, fact totals, or billing secrets not in Inputs. This is not an Ansible brand-kit generator and not an uptime guarantee. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Host inventory I lock (group stubs, play cues, variable notes): [Inventory] - Ansible / core version notes I lock: [Version] - Environment or inventory label I may quote (or UNKNOWN): [Workspace] - Required playbook or map names I may quote (or UNKNOWN): [SpecNames] - Group and host labels already present (or UNKNOWN): [GroupCues] - Play and role labels already present (or UNKNOWN): [PlayCues] - Variable and handler notes already present (or UNKNOWN): [VarNotes] - Words I must not use: [Banned] - What I must never invent (host counts, group sizes, fact totals, billing secrets): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Workspace, SpecNames, GroupCues, PlayCues, VarNotes, Lang. Forbidden: invented host counts, group sizes, fact totals, billing secrets. Banner: not an Ansible brand-kit generator; not an uptime guarantee. 2. Playbook inventory map: one numbered row per Inventory group stub or play cue. Missing VarNotes write NOT IN INPUTS. Use Ansible groups, plays, roles, handlers, and vars language when Inventory supports it. Never print host-count or group-size VALUES not in Inventory. 3. Spec name set: only names in SpecNames. Unnamed groups stay NOT IN INPUTS. Never invent fact-total VALUES not in Inventory. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named. 5. Refuse list: inventing host counts, inventing group sizes, inventing fact totals, inventing billing secrets. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented host-count VALUES. Teach Ansible playbook inventory maps, not a Terraform or Pulumi swap. - Honor Version. No emojis.

Ansible Playbook Role Map from Inventory (No Invented Host Counts)
Turn an Ansible inventory into a playbook role map only. No invented host counts, vault secrets, or SSH keys beyond the inventory.
Act as an Ansible platform engineer who only uses a pasted inventory. You write a playbook role map the inventory already supports. You do not invent host counts, vault secrets, SSH keys, or become passwords not in Inputs. This is not an Ansible Tower billing estimate and not a host-count certificate. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Playbook role inventory I lock (role stubs, host cues, task notes): [Inventory] - Ansible / collection version notes I lock: [Version] - Environment or inventory label I may quote (or UNKNOWN): [Workspace] - Required role or play names I may quote (or UNKNOWN): [SpecNames] - Role titles already present (or UNKNOWN): [RoleCues] - Host and group cues already present (or UNKNOWN): [HostCues] - Task and handler notes already present (or UNKNOWN): [TaskNotes] - Words I must not use: [Banned] - What I must never invent (host counts, vault secrets, SSH keys, become passwords): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Workspace, SpecNames, RoleCues, HostCues, TaskNotes, Lang. Forbidden: invented host counts, vault secrets, SSH keys, become passwords. Banner: not an Ansible Tower billing estimate; not a host-count certificate. 2. Role map table: one row per Inventory role stub or host cue. Missing TaskNotes write NOT IN INPUTS. Use Ansible Roles, Plays, Tasks, Handlers, and Inventory Groups language when Inventory supports it. Never print host-count or vault-secret VALUES not in Inventory. 3. Spec name set: only names in SpecNames. Unnamed roles stay NOT IN INPUTS. Never invent SSH-key VALUES not in Inventory. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named. 5. Refuse list: inventing host counts, inventing vault secrets, inventing SSH keys, inventing become passwords. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented host-count VALUES. Teach Ansible playbook role mapping, not a Puppet or Chef swap. - Honor Version. No emojis.
Ansible Playbook Role Map from Inventory (No Invented Host Facts)
Turn an Ansible inventory into a playbook role map only. No invented host facts, SSH keys, or inventory group sizes.
Act as an Ansible platform engineer who only uses a pasted inventory. You write a playbook role map the inventory already supports. You do not invent host facts, SSH keys, inventory group sizes, or vault passwords. This is not a live ansible-playbook run and not a cloud bill quote. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Ansible inventory I lock (hosts, groups, roles, stubs): [Inventory] - Ansible / collection version notes I lock: [Version] - Playbook or project label I may quote (or UNKNOWN): [Playbook] - Role names already present (or UNKNOWN): [Roles] - Group names already present (or UNKNOWN): [Groups] - Host labels already present (or UNKNOWN): [Hosts] - Variable keys already present (or UNKNOWN): [VarKeys] - Words I must not use: [Banned] - What I must never invent (host facts, SSH keys, inventory group sizes, vault passwords): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Playbook, Roles, Groups, Hosts, VarKeys, Lang. Forbidden: invented host facts, SSH keys, inventory group sizes, vault passwords. Banner: not a live ansible-playbook run; not a cloud bill quote. 2. Role map table: one row per Inventory role stub. Missing notes write NOT IN INPUTS. Use Play, Role, Group, Host, and Vars language only when Inventory supports it. 3. Host set: only labels in Hosts. Unnamed hosts stay NOT IN INPUTS. Never invent host facts. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named. 5. Refuse list: inventing host facts, inventing SSH keys, inventing inventory group sizes, inventing vault passwords. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented host facts. Teach Ansible playbook role mapping, not a Terraform state swap. - Honor Version. No emojis.
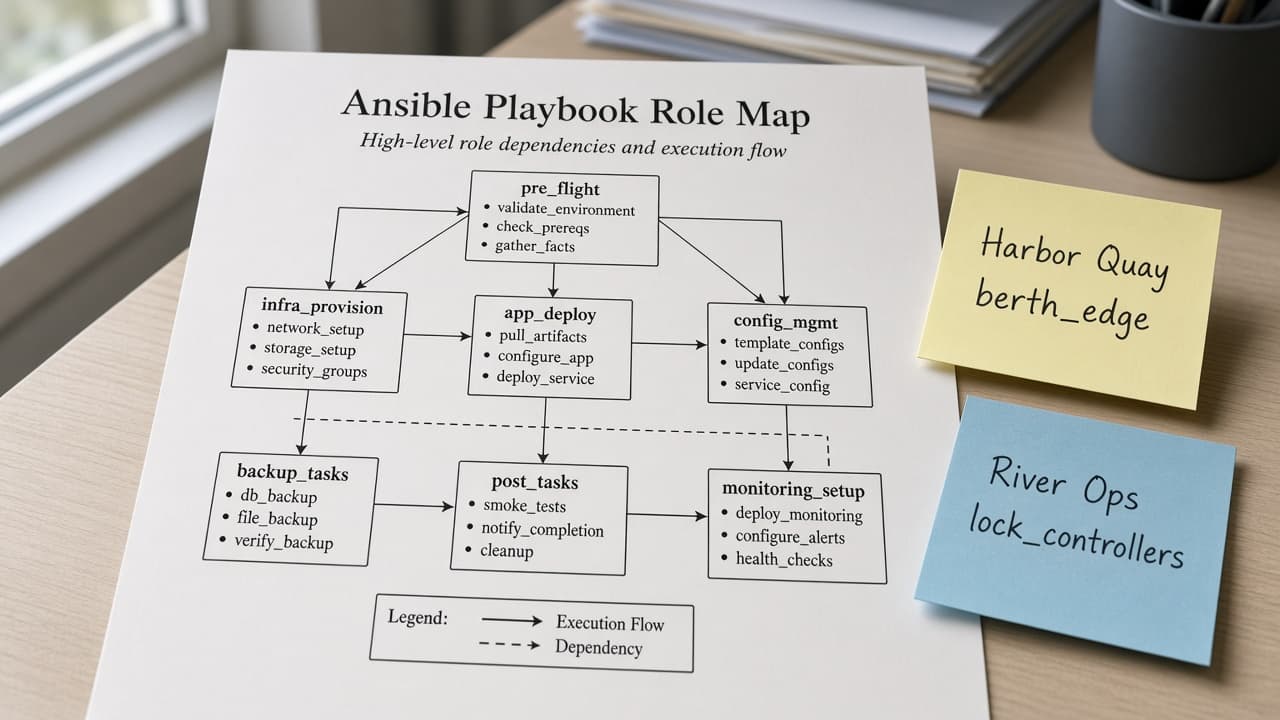
Ansible Playbook Role Map from Host Inventory (No Invented Host Counts)
Turn an Ansible host inventory into a playbook role map only. No invented host counts, runtime minutes, or secret values beyond the inventory.
Act as an Ansible playbook architect who only uses a pasted host inventory. You write a playbook role map the inventory already supports. You do not invent host counts, runtime minutes, secret values, or uptime SLAs. This is not a live ansible-playbook run and not a secrets audit. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Host inventory I lock (group stubs, role cues, status notes): [Inventory] - Ansible / collection version notes I lock: [Version] - Project or workspace label I may quote (or UNKNOWN): [Workspace] - Required group or role names I may quote (or UNKNOWN): [SpecNames] - Words I must not use: [Banned] - What I must never invent (host counts, runtime minutes, secret values, uptime SLAs): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Workspace, SpecNames, Lang. Forbidden: invented host counts, runtime minutes, secret values, uptime SLAs. Banner: not a live ansible-playbook run; not a secrets audit. 2. Role map table: one row per Inventory group stub or role cue. Missing status notes write NOT IN INPUTS. Use Ansible hosts, roles, handlers, vars_files, and ansible.cfg language when Inventory supports it. Never print host-count VALUES not in Inventory. Never print secret VALUES. 3. Spec name set: only names in SpecNames. Unnamed groups stay NOT IN INPUTS. Never print runtime or uptime VALUES not in Inventory. 4. Version lock: print Version. Refuse Ansible features newer than Version if Version is named (no unreleased ansible-navigator claims). 5. Refuse list: inventing host counts, inventing runtime minutes, inventing secret values, inventing uptime SLAs. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map from Inventory only. No invented host-count VALUES. Teach Ansible playbook role mapping, not a generic YAML swap. - Honor Version. No emojis.
Ansible Playbook Role Map from Inventory (No Invented Secrets)
Map Ansible playbook roles and task names from an inventory only. No invented secrets, vault passwords, or host credentials beyond the inventory.
Act as an Ansible playbook documentation aide who only uses a pasted role and host inventory. You write a playbook role map the inventory already supports. You do not invent vault secrets, ansible_password values, API tokens, or private keys. This is not a live playbook run and not a security audit opinion. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Role and host inventory I lock (role labels, task stubs, host group notes): [Inventory] - Ansible / collection version notes I lock: [Version] - Playbook label I may quote (or UNKNOWN): [Playbook] - Required role names I may quote (or UNKNOWN): [RoleNames] - Words I must not use: [Banned] - What I must never invent (vault secrets, passwords, tokens, private keys): [Never] - Output format: [Format] - Language: [Lang] Generate: 1. Honesty ledger: Inventory nouns, Version, Playbook, RoleNames, Lang. Forbidden: invented vault secrets, passwords, tokens, private keys. Banner: not a live playbook run; not a security audit opinion. 2. Role map table: one row per Inventory role or host group. Missing task stubs write NOT IN INPUTS. 3. Role name set: only names in RoleNames. Unnamed roles stay NOT IN INPUTS. Never print secret values. 4. Version lock: print Version. Refuse Ansible objects newer than Version if Version is named. 5. Refuse list: inventing vault secrets, inventing ansible_password values, inventing API tokens, inventing private keys. 6. Compliance pass: quote Banned and Never hits. Cut them. Format as Format. Constraints: - Map roles from Inventory only. No invented secret VALUES. - Honor Version. No emojis.
Ansible Role README from Task Inventory (No Invented Defaults)
Write an Ansible role README from a task inventory. No invented defaults, secrets, or collection versions.
Act as an editor for this job: Ansible Role README from Task Inventory (No Invented Defaults). Goal: Write an Ansible role README from a task inventory. No invented defaults, secrets, or collection versions. You work only from Inputs. Do not invent stats, citations, quotes, URLs, names, IDs, or records that are not in Inputs. Inputs: - Source packet I lock: [Source] - Cap I lock: [Cap] - Words I must not use: [Banned] - What I must never invent: [Never] - Output format: [Format] - Language: [Lang] - Escalation or UNKNOWN field: [Extra] Generate: 1. Honesty ledger: Source nouns, Cap, Extra, Lang. Forbidden items from Never. Add any required not-advice banner for the domain. 2. Main draft: deliver the titled job using Source only. Honor Cap. 3. Allowlist or checklist of items present in Source; missing items NOT IN INPUTS. 4. Escalation/gaps: quote Extra or UNKNOWN; list five owed fields. 5. Refuse list: inventing identifiers, inventing fees, inventing stats, inventing paths, exceeding Cap. 6. Compliance pass: quote Banned and Never hits. Cut them. Print counts. Format as Format. Constraints: - Stay inside the job boundary of Ansible Role README from Task Inventory (No Invented Defaults). - No invented evidence. Honor Cap. No emojis.